
Unique Encryption Keys
Unique encryption keys secure the communication between ONE Desktop, its local runtime, and your Ataccama Cloud environment. Each environment gets its own encryption key, provided as a keystore file that you generate in the Ataccama Cloud Portal, which is the Ataccama Cloud administration and configuration interface. The same keystore is used by the self-managed Data Processing Engines (DPEs) connecting to the environment.
This page describes how to generate the keystore and configure ONE Desktop and the local runtime to use it. For configuring a self-managed DPE to use the keystore, see Unique Encryption Keys in the ONE documentation.
How unique encryption keys protect your environment
Using unique encryption keys contributes to the overall security of your deployment in the following ways:
-
Provides additional protection against unauthorized access to your data and environment in Ataccama Cloud.
-
Keeps data encrypted and compliant with data protection regulations.
-
Helps mitigate data leakage risks and protects data in transit and at the edge of the network.
-
Secures communication between Ataccama ONE and edge components, such as self-managed DPEs and ONE Desktop.
Unique encryption keys can be rotated and securely backed up and restored without getting embedded in the backup.
The keys are stored in a Java Cryptography Extension (JCE) keystore file (keystore.jceks).
In the Helm values.yaml file generated by the Cloud Portal for Kubernetes-based DPE installations, the keystore is embedded as a Base64-encoded string.
Generate the keystore in the Cloud Portal
All edge components connecting to the same environment must use the same keystore.
If your environment is not managed through the Cloud Portal, contact Ataccama Support to obtain the keystore and its password.
To generate the keystore in the Cloud Portal:
-
In the Cloud Portal, go to your environment and switch to the Services tab.
-
In Shared Services, find ONE Desktop and select Instructions.
-
In Use keystore file, select Generate.
-
Once the keystore is ready, download the keystore file (Download keystore.jceks) and copy the corresponding password.
Keep the dialog open until you finish configuring all components in case you need to return to it. Otherwise, you have to generate a new keystore and password. 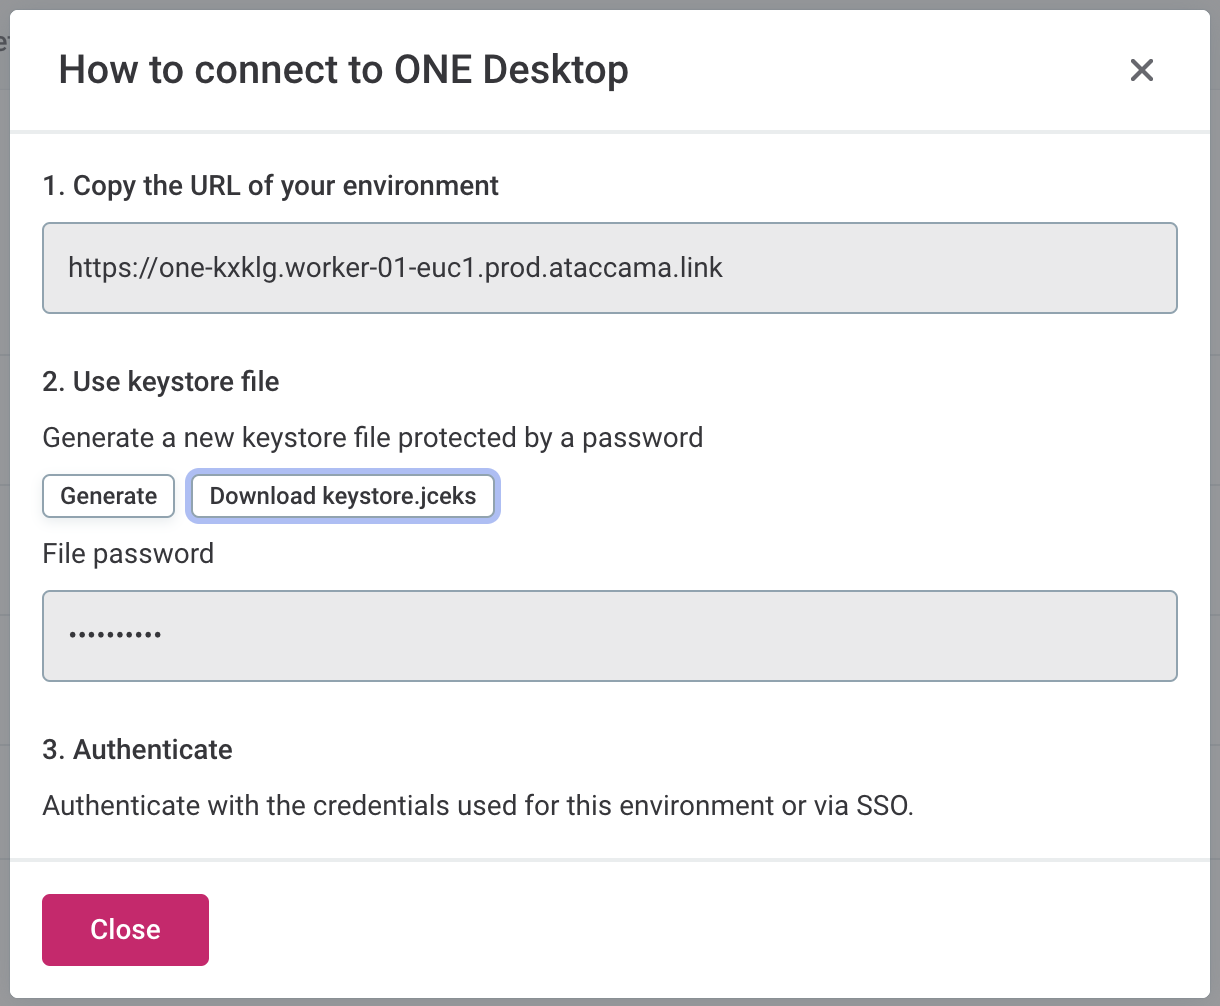
Configure ONE Desktop to use the keystore
-
Navigate to your ONE Desktop installation folder.
-
Open the
one-desktop.inifile in a text editor. -
Add the following properties. Make sure to provide the correct path to the downloaded keystore as well as the keystore password (see Generate the keystore in the Cloud Portal, step 4).
The key alias
initial_peripheralapplies to keystores generated in the Cloud Portal. If you obtained the keystore from Ataccama Support, use the alias provided with it.-Dproperties.encryption.keystore=[PATH_TO_DOWNLOADED_KEYSTORE_FILE] -Dproperties.encryption.keystore.password=[KEYSTORE_FILE_PASSWORD] -Dproperties.encryption.keyAlias=initial_peripheral -Dinternal.encryption.keystore=[PATH_TO_DOWNLOADED_KEYSTORE_FILE] -Dinternal.encryption.keystore.password=[KEYSTORE_FILE_PASSWORD] -Dinternal.encryption.keyAlias=initial_peripheral -
Save your changes.
-
To apply the properties to the local runtime, launch ONE Desktop.
-
Go to Window > Preferences > Java > Installed JREs.
-
Select the default JRE and then Edit.
-
In Default VM arguments, paste the properties listed in step 3.
-
Select Finish and then Apply and Close to save the changes.

Was this page useful?